cveDB
Local-first macOS vulnerability intelligence workstation and Cloudflare Edge archive indexing 408,000+ NVD CVEs, CISA KEV, and EPSS scores.
Shipping · v1.1.0
Platforms:
macOS 15.0+Universal2 (arm64 + x86_64)SQLite FTS5Cloudflare Edge
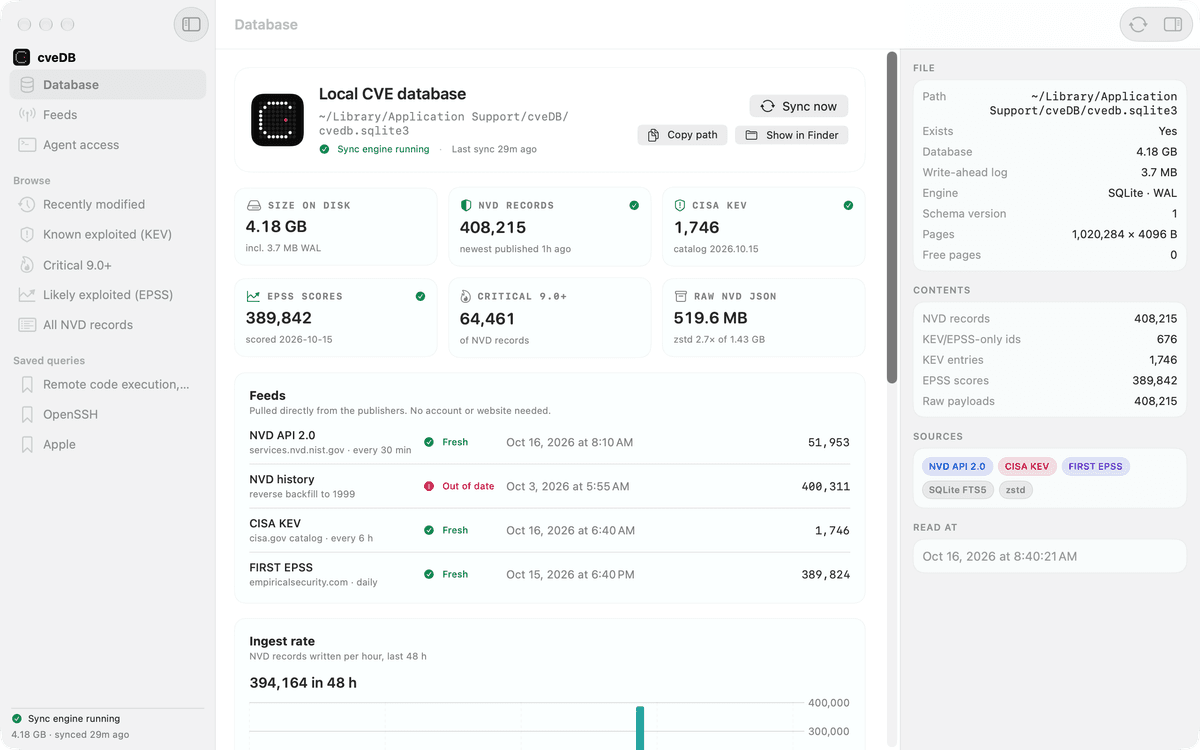
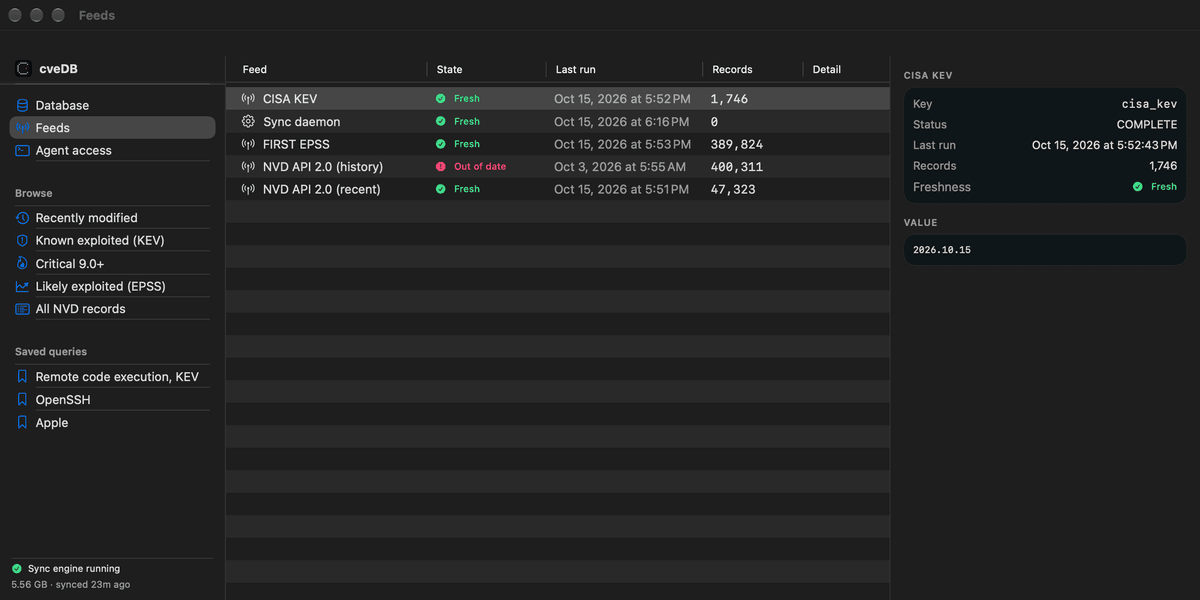
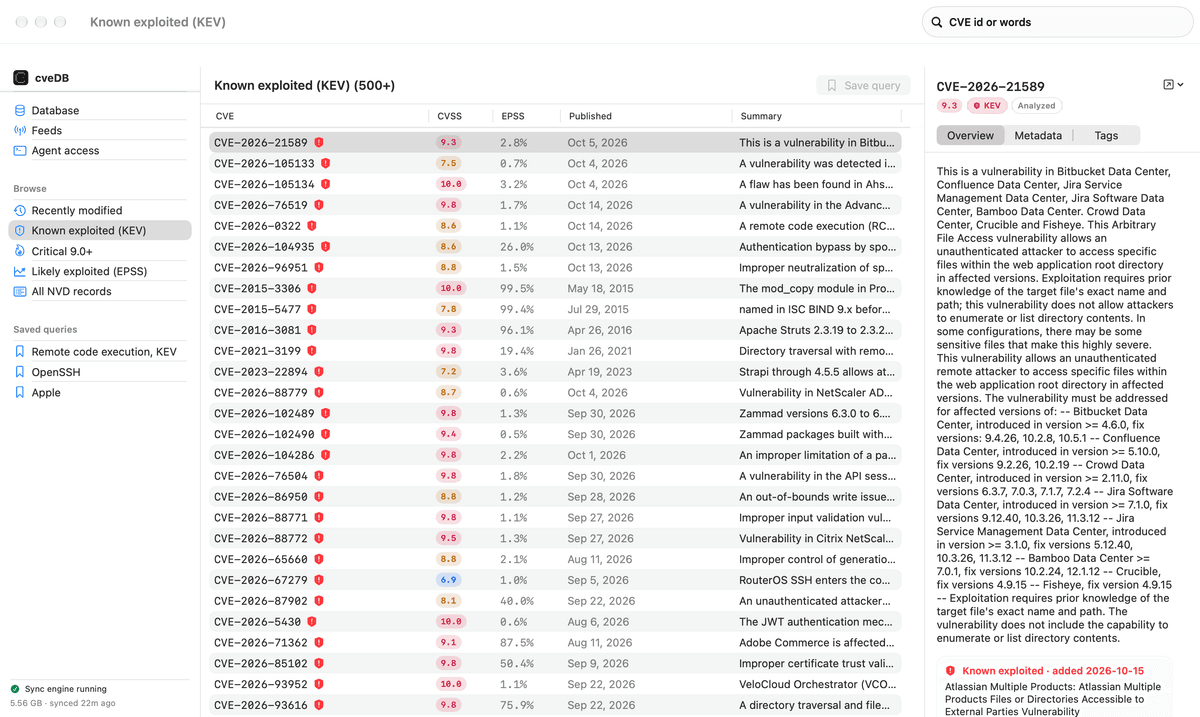
Application Screenshots
Captured on macOS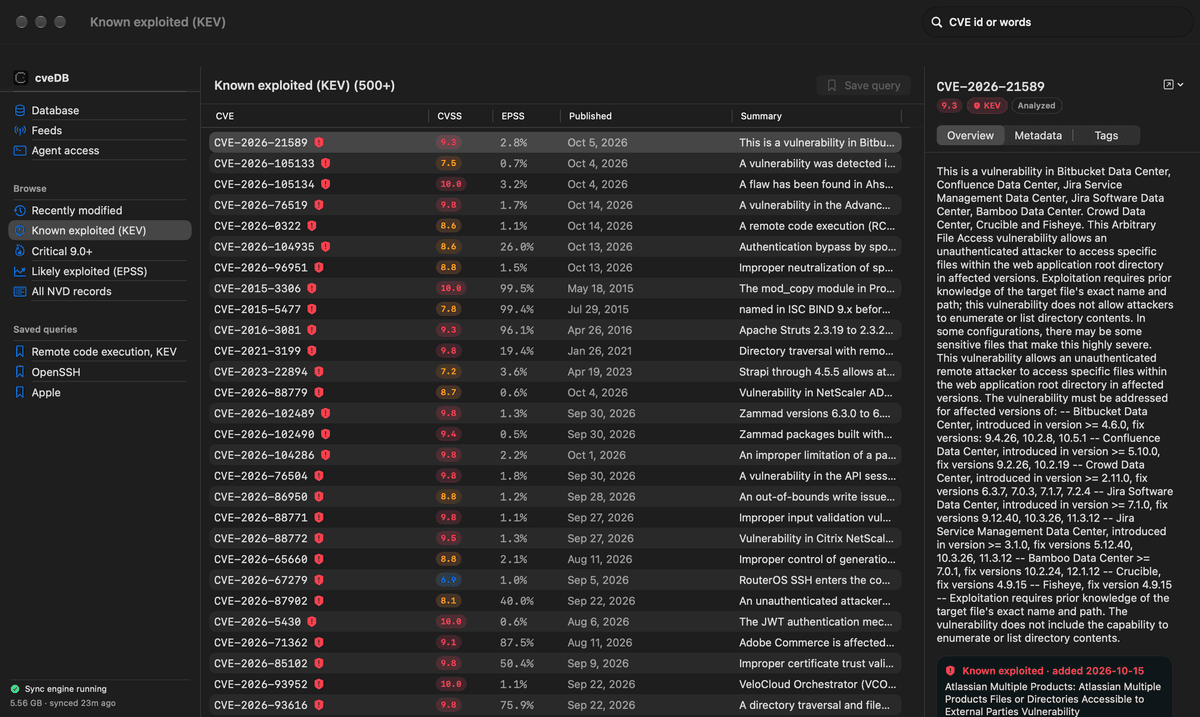
Key Features
- Complete offline vulnerability catalog (~4.18 GB SQLite WAL database) indexing 408,215 NVD CVE records and 592,692 CPE match rules
- Real-time tracking of 1,746+ CISA Known Exploited Vulnerabilities (KEV) and 389,842 FIRST.org EPSS 30-day exploitation probability scores
- Sub-10ms full-text search across CVE descriptions, CWE classifications, vendor CPE strings, and CVSS v3.1 / v4.0 vectors
- Automated incremental feed synchronization with cryptographic SHA-256 verification and offline snapshot export
- Built-in CLI and Model Context Protocol (MCP) server for local security auditing and automated dependency triage
- Companion high-speed web portal at cvedb.dev served from the Cloudflare global edge network
System Requirements
- Operating System
- macOS 15.0 (Sequoia) or later · Web portal accessible from any modern browser
- Architecture
- Universal2 binary (Apple Silicon arm64 & Intel x86_64)
- Code Signing
- Developer ID Application: east coast science, llc (ZU2882L4HT) · Apple Notarized
- Storage & Memory
- 25 MB application bundle · ~4.2 GB local SQLite vulnerability corpus
- Privacy & Network
- Zero query telemetry · All CVE lookups execute locally against on-disk SQLite
What's New
v1.1.0 (Build 8) ·- Expanded local corpus to 408,215 NVD CVEs, 1,746 CISA KEV entries, and 389,842 EPSS probability scores.
- Added dedicated Database Management view showing per-table row counts, index health, and storage paths.
- Added Agent & CLI Access inspector for one-click local MCP integration.
- Synchronized desktop release with the cvedb.dev Cloudflare Edge vulnerability tracker.
Local-First Vulnerability & Threat Intelligence for macOS and Cloudflare Edge
cveDB pairs a native SwiftUI macOS workstation application with the public cvedb.dev edge archive. Instead of relying on rate-limited external REST APIs during security audits or incident response, cveDB maintains a complete, deterministically indexed copy of the National Vulnerability Database (NVD), CISA Known Exploited Vulnerabilities (KEV) catalog, and FIRST.org Exploit Prediction Scoring System (EPSS) directly on your Mac's local SSD.
Architecture & Data Pipeline
- SQLite WAL + FTS5 Engine: Over 408,000 CVE records, 592,000 CPE product match rules, and 389,000 EPSS probability scores are stored in a single memory-mapped SQLite database with Write-Ahead Logging.
- Zero-Latency Triage: Full-text queries, CVSS v3.1/v4.0 severity filtering, and CISA KEV cross-referencing complete in under 10 milliseconds with zero outbound network traffic.
- Deterministic Feed Sync: Background delta synchronization pulls upstream NVD, CISA KEV, and EPSS updates on your schedule while preserving full offline capability for air-gapped or restricted networks.
- CLI & Agent Integration: Includes a native command-line tool and Model Context Protocol (MCP) endpoint so local build scripts and engineering agents can verify package advisories locally.